Block Headers vs Block Body: The Core Architecture of Blockchain
Nov, 14 2026
You might think a blockchain is just a giant list of transactions. But if you look under the hood, it’s actually two distinct things glued together: a tiny, dense block header and a much larger, variable-sized block body. Understanding the difference isn't just academic trivia; it’s the key to understanding why Bitcoin is secure, why Ethereum scales differently, and how your mobile wallet verifies payments without downloading gigabytes of data.
Think of a physical book. The block header is like the spine and the cover. It tells you what the book is, where it fits on the shelf (its link to the previous book), and provides a quick summary of its contents via a unique code. You can identify the book and verify it belongs in that specific spot on the shelf without ever opening it. The block body, on the other hand, is the actual pages inside. It contains all the stories (transactions). To read the story, you need the whole book. But to know the book is genuine and hasn’t been swapped out for a fake, you only need to check the spine (header).
The Anatomy of the Block Header
In Bitcoin, the block header is exactly 80 bytes. That’s it. No matter if the block contains one transaction or four thousand, the header size never changes. This fixed size is deliberate. It allows computers to process and verify the chain incredibly fast. Miners don’t hash the entire multi-megabyte block every time they try to solve the cryptographic puzzle; they only hash this 80-byte header. If they change even one bit in the body, the header changes, and their work is wasted. This separation saves massive amounts of computational power.
The header contains six critical fields that hold the metadata required to maintain the chain's integrity:
- Version Number (4 bytes): Indicates which set of software rules are being followed. Upgrades to the protocol often bump this number.
- Previous Block Hash (32 bytes): This is the cryptographic fingerprint of the previous block’s header. It creates the "chain" by linking each block backward to its predecessor.
- Merkle Root (32 bytes): A single hash that summarizes all transactions in the body. It proves that the transactions haven’t been tampered with.
- Timestamp (4 bytes): Records when the block was created. Note that this is approximate; nodes reject blocks with timestamps too far in the future or past.
- Difficulty Target (4 bytes): Tells miners how hard the cryptographic puzzle is. It adjusts roughly every two weeks to keep block times steady.
- Nonce (4 bytes): A random number miners tweak over and over again until they find a hash that meets the difficulty target.
This structure enables something called Simplified Payment Verification (SPV). When you use a lightweight wallet on your phone, you don’t download the full history of Bitcoin. Instead, you download just the headers. By checking the Merkle Root in the header against a small piece of data from the body, your wallet can confirm your transaction is valid without trusting anyone else.
The Role of the Block Body
If the header is the ID card, the block body is the vault. Its primary job is storage. In Bitcoin, the body starts with a transaction counter (a variable-length integer indicating how many transactions are included) followed by the list of transactions themselves. Each transaction includes inputs (where the money came from) and outputs (where the money is going).
Unlike the header, the body’s size varies wildly. Early Bitcoin blocks were tiny because there weren’t many users. Today, blocks can be up to 4 megabytes (or more, depending on SegWit weight calculations). Because the body is large and complex, verifying it requires more bandwidth and processing power than verifying the header. This is why full nodes-which store the entire blockchain-are heavier to run than light clients.
The body also handles the genesis block exception. The very first block in any blockchain has no previous block hash (it’s usually all zeros) and contains a special coinbase transaction that rewards the miner. While subsequent bodies just hold user transactions, the genesis body holds the initial distribution of coins.
How They Connect: The Merkle Tree Magic
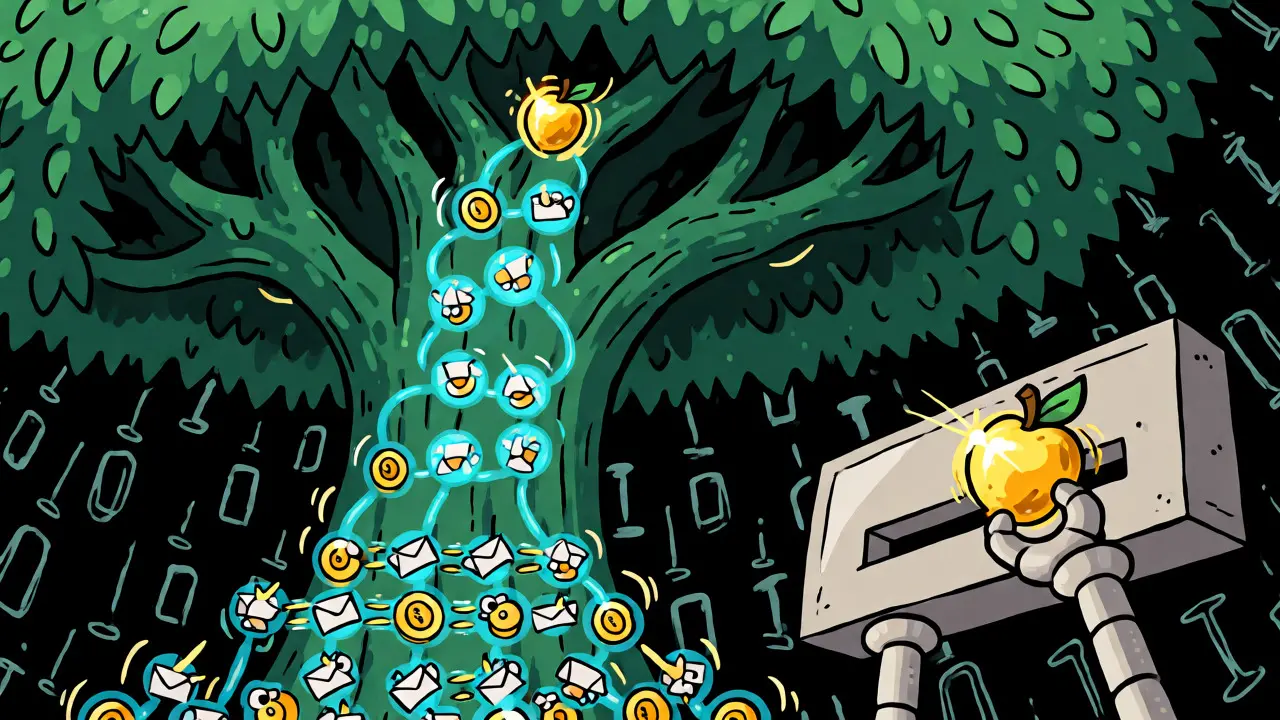
The bridge between the static header and the dynamic body is the Merkle root. Imagine you have ten transactions in a block. You pair them up and hash each pair. Then you take those five hashes, pair them up, and hash them again. You repeat this process until you’re left with one single hash at the top of the tree. This top hash is the Merkle root, and it gets embedded into the block header.
Why does this matter? Security. If someone tries to alter a transaction deep in the body-say, changing the recipient address-the hash of that transaction changes. That change ripples up the Merkle tree, altering the final Merkle root. Since the Merkle root is part of the header, the header itself changes. And since the header changes, its overall block hash changes. This breaks the link to the next block, alerting the network that the data has been tampered with. You can’t change the body without breaking the header, and you can’t change the header without breaking the chain.
Bitcoin vs. Ethereum: Structural Differences
While the concept of separating metadata (header) from data (body) is universal across blockchains, implementations vary significantly. Bitcoin sticks to the original minimalist design. Ethereum, however, needs to do more than just track value transfers; it tracks state (account balances, smart contract code, storage slots). Consequently, its structure is more complex.
| Feature | Bitcoin | Ethereum |
|---|---|---|
| Header Size | Fixed 80 bytes | Approx. 500 bytes |
| Hash Function | SHA-256 | Keccak-256 |
| Body Content | Transactions only | Transactions + Uncle Blocks (Ommers) |
| State Tracking | UTXO model (implied by transactions) | Explicit State Root in header |
| Consensus Impact | Miners hash header for PoW | Validators sign header for PoS |
Ethereum’s header includes extra fields like the State Root, Transaction Root, and Receipts Root. These roots allow light clients to verify not just that a transaction happened, but that the resulting account balance is correct. However, this comes at a cost: Ethereum’s headers are larger, meaning light clients must download more data to perform the same basic verification tasks compared to Bitcoin.
Why Developers Care About This Split
If you’re building an app, the header-body distinction dictates your architecture. For a simple payment gateway, you might only need to monitor headers to detect new blocks and then query a third-party API for transaction details. This keeps your server costs low. But if you’re building a decentralized exchange that needs to know the exact state of every smart contract, you likely need to run a full node that processes both headers and bodies continuously.
There’s also the issue of pruning. Old block bodies are less useful once the UTXOs (Unspent Transaction Outputs) they created have been spent. Many nodes prune the old bodies to save disk space but keep all headers forever. This ensures the chain remains verifiable while reducing storage requirements from hundreds of gigabytes to a manageable level. Without this separation, we’d be forced to store every byte of historical data indefinitely, making blockchain nodes prohibitively expensive for average users.
Common Misconceptions
A frequent error among beginners is thinking that miners hash the entire block. They don’t. As noted by developer Marco Falke in Bitcoin Core commits, miners spend 99.9% of their effort hashing the 80-byte header. If they had to hash the entire 1MB+ body for every attempt, mining would be orders of magnitude slower and less energy-efficient.
Another myth is that the timestamp in the header represents the exact moment the block was mined. It doesn’t. It’s a suggestion made by the miner who found the block. Other nodes accept it as long as it’s within a reasonable range of their own clocks. This flexibility prevents network stalls due to minor clock drifts across thousands of global servers.
The Future of Block Structure
The header-body dichotomy isn’t static. Ethereum is currently moving toward Verkle Trees, which will drastically shrink the proof sizes needed to verify parts of the state, effectively making headers even more powerful for light clients. Meanwhile, Bitcoin’s Taproot upgrade already tweaked how scripts are hashed into the Merkle root, improving privacy and efficiency.
As Layer 2 solutions like Lightning Network roll up thousands of transactions off-chain, the main chain’s block bodies become smaller and simpler, while headers remain the anchor of security. The trend is clear: keep the body lean, make the header smart. Understanding this balance helps you grasp why some chains feel slow (large bodies, heavy verification) while others feel instant (small bodies, optimized headers).
What happens if I change a transaction in the block body?
Changing a transaction alters its hash. This change propagates up the Merkle tree, modifying the Merkle Root. Since the Merkle Root is part of the block header, the header’s hash changes. This breaks the cryptographic link to the next block in the chain, invalidating the entire sequence of subsequent blocks unless they are re-mined.
Why is the Bitcoin block header only 80 bytes?
The 80-byte size is fixed to optimize performance. It allows miners to rapidly test billions of nonce values per second without processing large amounts of transaction data. It also enables lightweight SPV wallets to sync quickly by downloading only headers instead of the full multi-gigabyte blockchain.
Does Ethereum use the same block structure as Bitcoin?
No. While both separate headers and bodies, Ethereum’s header is larger (~500 bytes) and includes additional fields like State Root and Receipts Root to support smart contracts and account states. Ethereum also uses Keccak-256 hashing instead of SHA-256 and includes uncle blocks in the body to improve security during forks.
Can I verify a transaction using only the block header?
Not entirely. You need the block header to verify the block’s position in the chain and its validity via Proof-of-Work. However, to verify a specific transaction, you need the Merkle Proof-a small subset of hashes from the body-that links that transaction to the Merkle Root stored in the header.
What is the role of the Nonce in the block header?
The Nonce is a 4-byte field that miners adjust repeatedly to find a block hash that is lower than the current difficulty target. It is the primary variable manipulated during Proof-of-Work mining. Once a valid Nonce is found, the block is considered solved and broadcast to the network.